Showing posts with label technology. Show all posts

Sunday, August 28, 2016

Drones from Swedish Church to Drop Thousands of Bibles in Iraq to Convert ISIS

An evangelical church from Sweden is planning to drop thousands of electronic Bibles to areas controlled by the Islamic State in Iraq. With the goal of spreading the word of God, the church will be using drones to distribute Bibles in hopes of converting the locals to Christianity. 

An evangelical church from Sweden is planning to drop thousands of electronic Bibles to areas controlled by the Islamic State in Iraq. With the goal of spreading the word of God, the church will be using drones to distribute Bibles in hopes of converting the locals to Christianity.

"Our ambition is to pass on the hope and love of the Christian Gospel to a population living in closed areas where they are being denied human rights," Livets Ord Church mission director Christian Ã…kerhielm told in an interview with Swedish TV channel SVT.

The Swedish church Livets Ord, or "Word of Life," is set to start its project in the next few weeks. By utilizing a tactic that simulates the airstrikes that have traumatized many people in the ISS-controlled areas, the church aims to bring light and hope to Muslims.

The Bibles that will be delivered are translated into Arabic. Also, they are electronic but don't need to be plugged in to work.

Word of Life church also said its congregations and affiliated organizations have testified that there is a huge spiritual awakening now in the Middle East. It added that thousands of people turn to Jesus and the need for Bible is very huge.

The evangelical church was established in 1983. It has a huge congregation in the city of Uppsala, an hour's drive north of the Swedish capital, Stockholm. The drone mission was introduced by the church's charismatic preacher Joakim Lundqvist.

According to its website, Word of Life church is a home for people from all walks of life. It is also a place where people come together to talk about Christ and one another. One of the missions of the church is to reach the corners of the globe to preach the Gospel.

As of now, ISIS is believed to be holding 3,500 people as slaves, CNN reports. Most of the enslaved are woman and children from the Yazidi community. There also reports that the group has Christian hostages.

ISIS aims to establish an Islamic state called a caliphate across Syria, Iraq and beyond. Even though the terror group is reportedly losing its territory in Iraq and Syria, where it mainly operates, it has still over 22,000 fighters despite thousands of airstrikes by the international coalition led by the United States.
 

Tuesday, August 9, 2016

Nintendo’s NES Classic Edition will add saving throughout gameplay


Sorry purists: New players of classic NES games on the upcoming micro NES classic Edition system from Nintendo won’t have to rely on barbaric codes that recall progress, or single session playthroughs to beat games.
Speaking with French language radio show La Terrasse ENERGIE (via IGN) Nintendo of Canada comms person Julie Gagnon told listeners that the console will provide players with permanent save points, like more sophisticated games from the SNES and later era, as well as a temporary, instant save feature that lets you quickly capture and restore your game state so you can go to the bathroom, feed your child or bathe yourself without leaving the console running as in days of old.
The new console, which ships with 30 classic games pre-installed, will also offer a “pixel perfect” display mode that shows each pixel from the original as a solid color square, instead of fuzzying things up via anti-aliased upscaling. It will also offer the option to play in classic 4:3 ratio, and has a simulation feature that mimics playing on classic bubble-fronted CRT TVs.
So with pixel perfect visuals, there’s actually something here to please purists, too. And personally, I’m thrilled you’d be able to save. Maybe I’ll finally be able to beat some of the classics I never had the patience for as a kid. I’ll definitely try when the console comes out on November 11.

‘Smart’ locks yield to simple hacker tricks


It’s an open secret that the Internet of Things (if we must call it so) is pretty terrible, whether in standards, interoperability or security. You don’t really expect good security in a smart light bulb or coffee maker, though. A smart front door lock, however, really shouldn’t be quite this easy to hack.
Two different presentations at DEF CON this year made it clear that there’s a long way to go before we should start trusting the average smart lock — or even the nice ones (though if you had to choose, the latter is the better). This may surprise you, or you might have been saying it for years. At all events, these guys proved it with gusto.
Anthony Rose and Ben Ramsey, from Merculite Security, showed off a bit of lock hacking done with less than $200 worth of off-the-shelf hardware. Some opened easier than others, but in the end 12 out of 16 yielded.
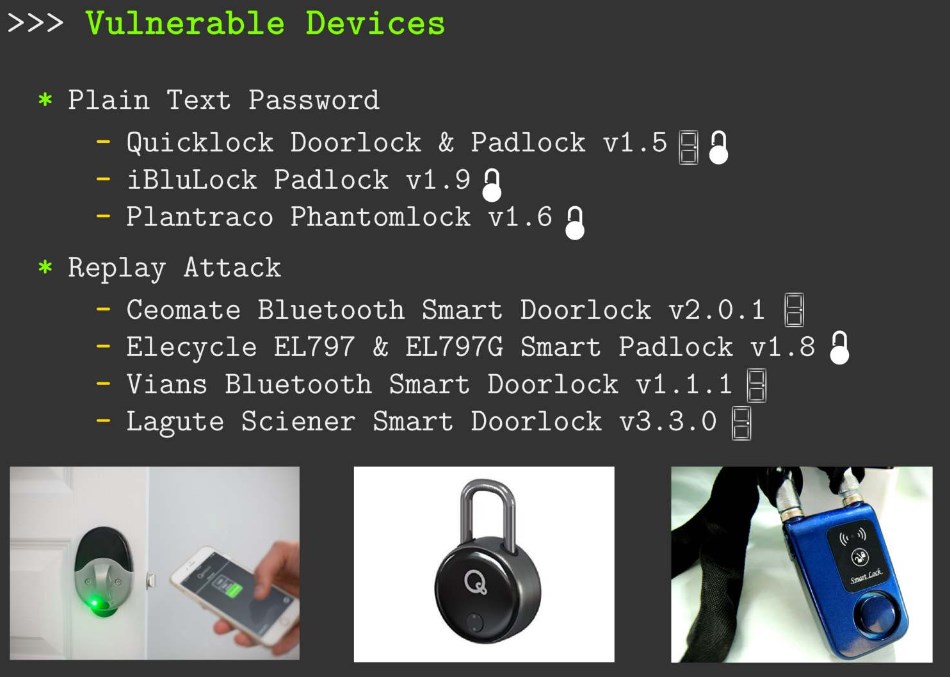
Locks from Quicklock, iBluLock, and Plantraco transmitted their passwords in plaintext, making them vulnerable to anyone with a Bluetooth sniffer. Others were tricked by the attacker simply replaying the same data they snatched out of the air when a legit user unlocked the door. Another entered a failstate and opened by default when it received an encrypted string that was off by one byte.
vulnerable_locks
Worth noting as well: doing a bit of wardriving, the two found plenty of locks identifying themselves as such, making it easy for an attacker to find devices to listen in on.
This was a pretty poor showing altogether, although a few resisted Rose and Ramsey’s attempts: the Noke and Masterlock smart padlocks survived, and a Kwikset Kevo did as well — until they opened it with a screwdriver. Okay, that’s cheating, but the point stands.
Perhaps of most concern, only one of the 12 vendors the two contacted to inform them of these flaws responded — and even then, there was no plan to fix anything.
One that Merculite failed to crack was the August door lock, a rather more well known brand than the others (MasterLock notwithstanding). Fortunately, someone else had already made it their mission to break the thing wide open.
Jmaxxz's entertaining, meme-filled presentation puts the lie to many of the claims set forth by August, and although it’s unlikely your average B&E artist is going to bother to circumvent certificate pinning and pawing through your logs, the security holes are real.
Many items that were too hard to get by ordinary hacking means like sniffers… could be found in plaintext in logs and the like. Jmaxxz is one of those hackers that doesn’t like to work any harder than he has to — and why should he?
Inside the August there were good practices and bad — and to the company’s credit, the hacker noted, they have been responsive and many of these holes are likely fixed by now. Still, it’s hard to believe that guests could ever award themselves extra lock permissions just by changing a string in the API calls from “user” to “superuser”!
For now, it seems, these locks are long on convenience and short on security. If you don’t mind having less-than-stellar security on your pool house or mother-in-law, this could be a nice way to keep your keychain light — but for the front door, you can do better.